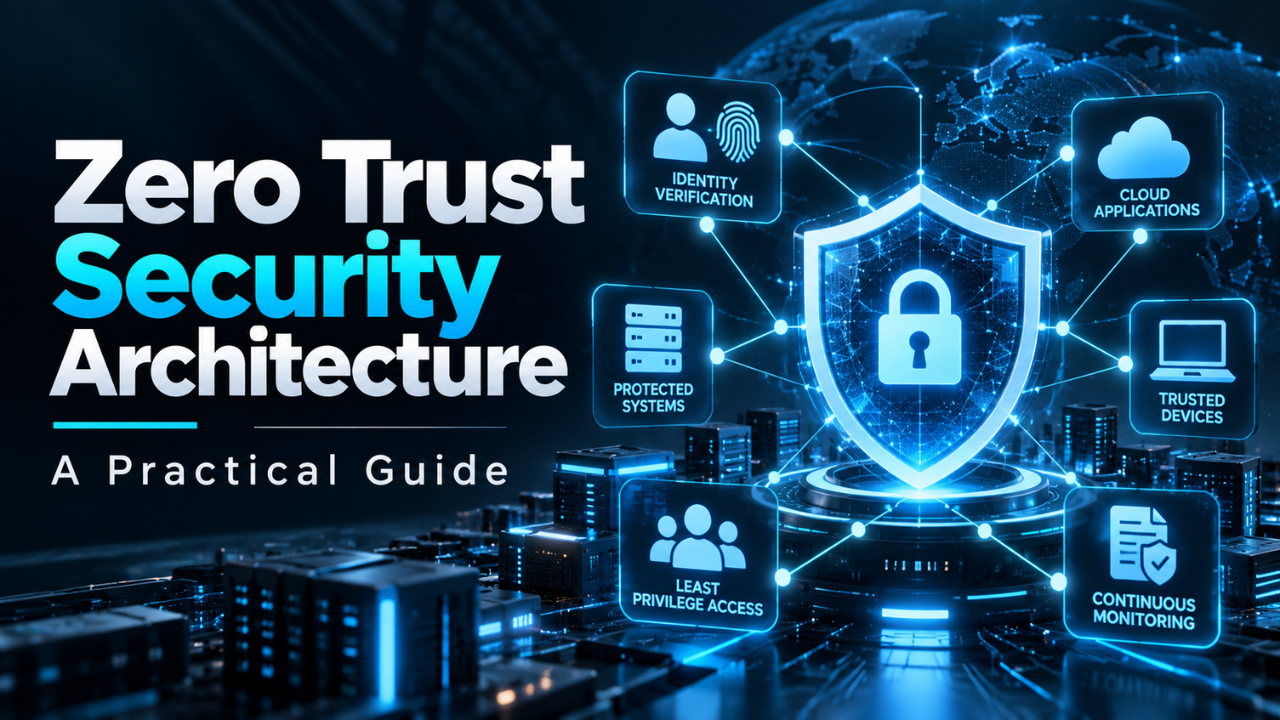
Zero Trust Security Architecture: A Practical Guide
A staff member signs in from the office, but their password was stolen yesterday. Should the office network automatically make them trustworthy? In a traditional setup, it sometimes does. That assumption is one reason modern security teams are rethinking where they draw the line.
Zero Trust Security Architecture changes the question. Instead of trusting a connection because it comes from a familiar network, it checks who or what is requesting access, which resource they need, and whether the request meets current policy. It’s a practical approach for organizations whose people, apps, and data now work across offices, homes, and cloud services.
Table of Contents
- What Zero Trust Security Architecture Means
- Why the Old Network Perimeter Is Not Enough
- Core Components of a Zero Trust Architecture
- What an Access Decision Looks Like
- How to Build a Zero Trust Program
- Mistakes That Make Zero Trust Harder
- What Zero Trust Can and Cannot Do
- A Practical Approach to Understanding Zero Trust
What Zero Trust Security Architecture Means
Zero trust is a way to design security around resources—such as files, applications, databases, and services—instead of relying on a broad network boundary. A person doesn’t gain access simply because they’re inside the company network, and a device doesn’t become trusted just because the company owns it. Each access request needs to meet the relevant policy.
NIST describes zero trust as an approach that removes implicit trust based on a user’s or device’s network location or ownership. It also frames authentication and authorization as distinct checks made before a session to a resource is established.
That doesn’t mean employees are treated as suspects. It means access is granted for a specific reason and limited to what the person or system needs. A payroll specialist may need the payroll application, for example, without needing access to the company’s source code repository.
Zero trust is also not a single product. Identity systems, device management, network controls, application policies, and monitoring can all play a part. The architecture is the set of rules and controls that makes those pieces work together.
Why the Old Network Perimeter Is Not Enough
For a long time, companies could put most systems inside an office network and treat the firewall as the main gate. That model is harder to rely on when staff work remotely, business software runs in the cloud, and contractors or partners need access to selected tools.
A trusted connection can also be compromised. An attacker might steal an employee’s password, take control of an unattended laptop, or exploit a vulnerable service. If the first successful sign-in gives broad access to a flat internal network, the attacker may be able to move from one system to another.
Zero trust addresses this problem by making network location only one possible signal in an access decision. The user, their device, the application, and the sensitivity of the data matter too. NIST’s guidance specifically focuses protection on resources rather than network segments, reflecting how distributed work and cloud services have changed the shape of company networks.
Core Components of a Zero Trust Architecture
A useful way to understand the architecture is to follow a request. Someone tries to open a business application. A policy decision system checks the request, then a control point either allows the connection or blocks it.
NIST’s model describes three key logical parts. The policy engine decides whether access should be granted based on the organization’s rules and available information. The policy administrator carries out that decision by setting up or ending the connection. The policy enforcement point sits between the requester and the resource, enforcing the decision. These functions might be delivered by different systems, or grouped together in a security platform.
The decision needs reliable information. Identity services can confirm who a person is and what role they have. Device management can report whether a laptop is enrolled, encrypted, and up to date. Application and data inventories help teams define which resources exist and who should use them. Monitoring supplies context, such as whether an account has recently shown unusual behavior.
In a cloud application, the architecture may need to check service identities as well as human users. For example, a reporting service might need to read sales data but have no reason to access employee records. NIST’s cloud-native guidance describes using identity-based policies for applications and services across hybrid and multicloud environments.
Network segmentation can still help. It can limit which systems can communicate and reduce opportunities for an intruder to move around. Zero trust simply makes clear that segmentation alone doesn’t establish who or what should have access.
What an Access Decision Looks Like
Imagine an employee opens the company’s finance system from home. The system confirms their identity, checks that they’re allowed to use the finance app, and looks at the device’s security status. If the laptop is managed and healthy, the employee may get access to the functions required for their job.
Now suppose the same account tries to connect from an unknown device, or suddenly attempts to export a large set of records. The organization can require an additional check, restrict the action, or block access while someone investigates. The response depends on the organization’s policy and the resource’s sensitivity.
The goal is not to ask users for a new password every few minutes. It’s to make access decisions based on useful signals and limit exposure when risk changes. That requires clear rules. “Allow employees into the finance app” is broad; “allow members of the finance team to view records on a compliant device, with exports restricted to approved roles” gives the system something more meaningful to enforce.
How to Build a Zero Trust Program
Start with a resource that matters and a problem you can describe clearly. A company might choose its payroll system because it contains sensitive information, or its remote access service because too many users currently receive broad network access.
Before buying or configuring tools, map the people, devices, services, and data involved. Find out who owns the resource, who actually uses it, and what access they need. In many organizations, this inventory work reveals dormant accounts and permissions that were never removed after someone changed roles.
Next, tighten identity and device checks. Use multifactor authentication, especially for sensitive access, and make sure access policies account for device health where practical. Review administrative accounts separately: people who manage systems should use elevated access only when needed, and their privileges should be limited to the task.
Then protect the resource itself. Replace broad network permissions with narrower application or data policies where possible. Segment systems that have different security needs. For cloud-native applications, define which services can communicate and which data each service can reach.
Finally, collect logs that help you see whether the rules are working. A policy that blocks legitimate work will encourage people to find a workaround; one that quietly allows suspicious activity provides little protection. Review access denials, unusual sign-ins, support requests, and exceptions. Adjust the policy based on what those signals show.
This is best done in stages. Pilot one application or user group, fix the rough edges, and expand from there. CISA’s Zero Trust Maturity Model is designed to help organizations shape a staged strategy and implementation plan. NIST’s 2025 implementation guide also offers examples built across on-premises and cloud environments, which can help teams compare design approaches.
Mistakes That Make Zero Trust Harder
A common mistake is treating multifactor authentication as the whole project. MFA is valuable, but it can’t tell you by itself whether a device is secure or whether a user should be able to download a particular file. Identity is one part of a broader access decision.
Another mistake is trying to redesign every system at once. Legacy applications may not support modern identity controls, and a rushed migration can disrupt important work. A phased approach gives teams room to test policies, document exceptions, and improve the design.
Overly strict rules can create their own problems. If a legitimate employee is repeatedly blocked from essential work, they may start sharing accounts or moving information to unapproved tools. Make it easy to report access problems, and give administrators a controlled way to investigate and resolve them.
It’s also easy to overlook non-human identities: service accounts, software integrations, and automated jobs. These can have long-lived credentials and broad permissions. Include them in inventories and access reviews; an architecture that checks human sign-ins but ignores services leaves a significant gap.
What Zero Trust Can and Cannot Do
A well-designed zero trust architecture can reduce unnecessary access and make it harder for an attacker to move freely after compromising an account or device. It can also help organizations apply consistent policies across offices, remote connections, and cloud environments. NIST notes that zero trust is intended to protect distributed resources while supporting access from different locations and devices.
It won’t prevent every breach. A user can still be tricked, a device can still be vulnerable, and a policy can still be misconfigured. Zero trust depends on accurate identity data, useful monitoring, and regular reviews. It also takes time: older applications may require adapters or gradual changes before they can follow the same access rules as newer services.
Think of it as a way to reduce how much damage one successful compromise can cause—not as a guarantee that compromise won’t happen.
A Practical Approach to Understanding Zero Trust
Zero Trust Security Architecture replaces broad assumptions with specific access decisions. It asks whether this user, on this device, should reach this resource under these conditions—and keeps the permission narrow enough to match the need.
The strongest starting point is a real business resource, a clear access policy, and a small pilot that teams can learn from. Expand as identity records, device checks, application controls, and monitoring improve. Over time, the organization gains a more deliberate way to protect its data without making every connection depend on an old idea of a trusted network.